CVE Program Funding Reinstated: Implications for Global Cybersecurity and the Road Ahead
The CVE Program’s funding has been reinstated, ensuring continued global vulnerability tracking. A new CVE Foundation now aims to secure…
The CVE Program’s funding has been reinstated, ensuring continued global vulnerability tracking. A new CVE Foundation now aims to secure…
Critical FortiSwitch vulnerability (CVE-2024-48887) allows unauthenticated password changes – patch now or apply mitigation steps immediately
A massive breach hit Oracle Cloud, exposing 6M records and affecting 140K+ tenants. Exploiting a known vulnerability, the attacker demands…
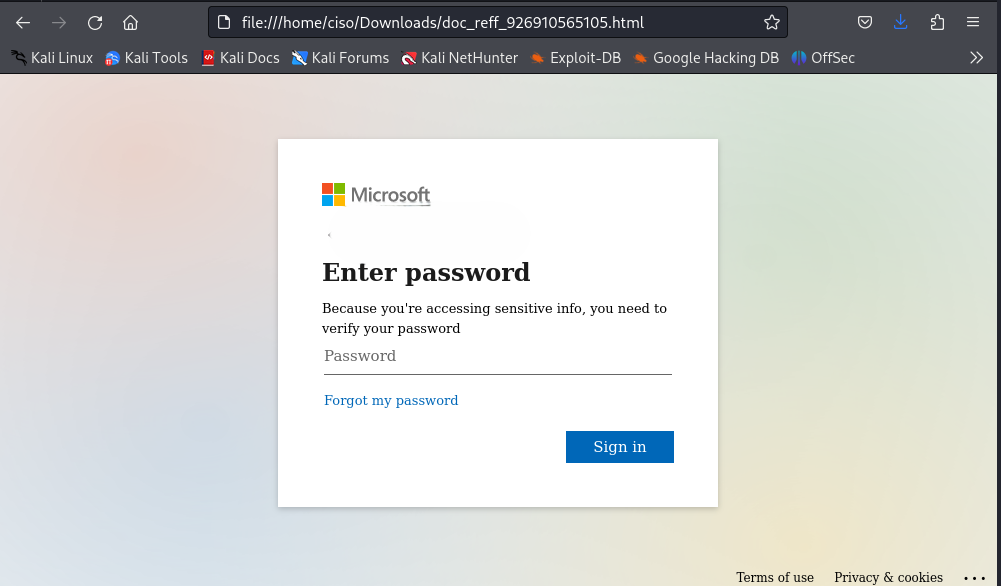
Hackers are increasingly using HTML attachments in phishing emails to bypass security filters and steal user credentials. This article explores…
The $1.5B Bybit hack has been traced to North Korean Lazarus Group via a supply chain attack on Safe{Wallet}. The…
Microsoft will end support for Exchange 2016 & 2019 on October 14, 2025—no more security patches, updates, or support. Businesses…
The Digital Operational Resilience Act (DORA) is a cornerstone of the EU’s Digital Finance Strategy, aiming to bolster financial entities’…
The NIS2 Directive (Directive (EU) 2022/2555) is a game-changer for cybersecurity in the European Union, expanding regulatory oversight, increasing enforcement,…